
What Is the US Data Privacy Patchwork?
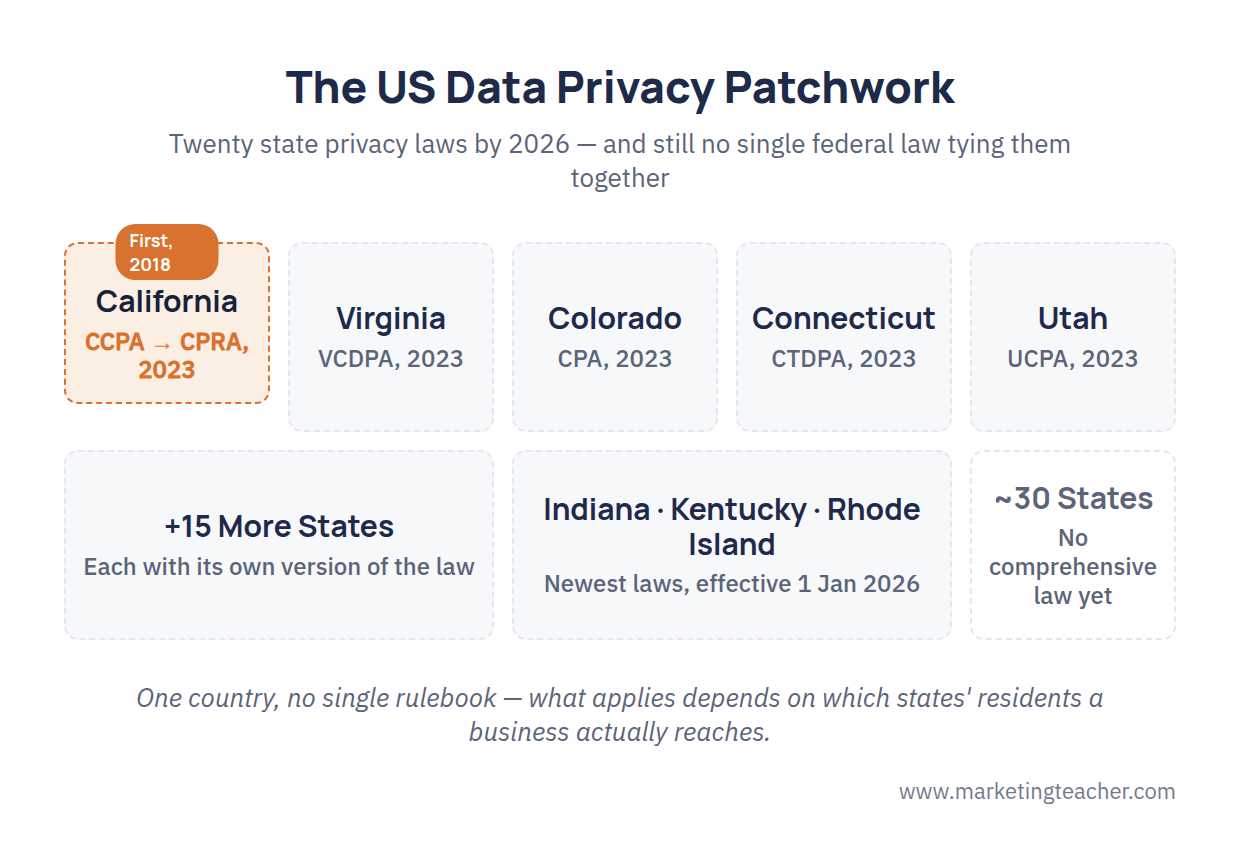
Ask a marketer in London, Dublin or Toronto which privacy law applies across the European Union and the answer is simple: the GDPR, one regulation covering 27 countries. Ask the same question about the United States, and there is no equivalent single answer. The US has never passed a comprehensive federal privacy law. Instead, individual states have written their own rules, one legislature at a time, since California passed the first in 2018. By 2026, twenty states had enacted a comprehensive consumer privacy law of their own (MultiState, 2026), each with its own thresholds, rights and penalties. Marketers who sell into the US, or collect data from US visitors, now have to comply with whichever of these laws apply to their business, sometimes several at once. This “patchwork” is the defining feature of US privacy regulation, and it is the opposite of the single-rulebook approach used elsewhere.
No Federal Law, Fifty Different Legislatures
The US does have federal privacy rules, but they are “sectoral” rather than comprehensive: HIPAA covers health records, the Gramm-Leach-Bliley Act covers financial data, and the Children’s Online Privacy Protection Act (COPPA) covers under-13s online. None of these cover the ordinary marketing data most businesses collect, such as email addresses, browsing behaviour or purchase history. Congress has tried repeatedly to fill that gap. The most serious recent attempt, the American Privacy Rights Act (APRA), was circulated as a bipartisan discussion draft in April 2024 but stalled over disagreements on whether it should override state laws and whether consumers should be able to sue directly (Wiley, 2024). Further bills were introduced in the new Congress for 2025 to 2026, but as of this lesson none has become law. Until one does, privacy regulation in the US is being written state by state, not in Washington.
California Leads: From CCPA to CPRA
California moved first. The California Consumer Privacy Act (CCPA) took effect in 2020, giving residents the right to know what personal information a business holds, to delete it, and, crucially for marketers, to opt out of its “sale.” Voters then strengthened the law in November 2020 by passing the California Privacy Rights Act (CPRA) as a ballot initiative, which took full effect on 1 January 2023. The CPRA created a dedicated regulator, the California Privacy Protection Agency (CPPA), added a right to opt out of data “sharing” for cross-context advertising (closing a loophole some companies had used to avoid the word “sale”), and introduced extra protections for sensitive categories such as precise location and health data. Penalties scale with intent: the CPPA and the state Attorney General can each fine a business up to $2,663 per violation, rising to $7,988 for an intentional violation or one involving a child’s data, figures that are adjusted for inflation every two years (CPPA, 2024). The two regulators cannot both penalise the same breach (IAPP, 2021).
The Fast Followers: Virginia, Colorado, Connecticut and 2026’s New Arrivals
Virginia passed the second comprehensive law, the Consumer Data Protection Act (VCDPA), in 2021, taking effect in 2023. It broadly follows California’s opt-out structure for sales and targeted advertising, but goes further for sensitive personal data, such as race, precise geolocation and health information, which may only be processed after the consumer gives clear, affirmative, opt-in consent (Loeb & Loeb, 2021). Colorado’s Privacy Act and Connecticut’s Data Privacy Act followed within a year, each adding small but real differences: Colorado, for example, writes into its statute a requirement to honour a universal opt-out signal sent automatically by the consumer’s browser, rather than just offering a link to click. By the start of 2026, the list had grown to twenty states, with Indiana, Kentucky and Rhode Island’s laws taking effect on 1 January that year alone. More are likely, since new bills are introduced in multiple state legislatures every year, a trend that sits in sharp contrast to the single, centrally-enforced models used elsewhere, such as China’s PIPL.
Opt-Out Versus Opt-In: Why the Model Matters
The single biggest structural difference between the US approach and Europe’s data protection laws is the default setting. Under the EU and UK’s GDPR regimes, a business generally needs the consumer’s affirmative consent before it processes personal data at all, an opt-in model. Under most US state laws, a business can collect and even sell personal data by default, and the consumer has to actively exercise a right to opt out. This is why nearly every CCPA-covered website now carries a “Do Not Sell or Share My Personal Information” link: the law assumes “yes” unless the visitor says otherwise, a sharp contrast with the GDPR’s consent-first approach. The gap is narrowing in one respect, since states increasingly require opt-in consent for sensitive categories, as Virginia does, but for ordinary marketing data, opt-out remains the American default, and that single design choice shapes everything from cookie banners to email list-building strategy for any business operating on both sides of the Atlantic.
Summary
The United States regulates data privacy through a patchwork of state laws rather than one federal statute. California’s CCPA and CPRA set the template in 2018 and 2020, built around a right to opt out of data sale and sharing rather than the opt-in consent model used elsewhere. Virginia, Colorado, Connecticut and a steadily growing list of other states, twenty in total by 2026, have each passed their own versions, with real variation in thresholds, universal opt-out requirements and sensitive-data rules. For any marketer collecting data from US customers, the practical question is never “does US privacy law apply to me?” but “which states’ laws apply, and what do they each require?” This is general education, not legal advice; a business operating in the US should confirm its specific obligations with a qualified privacy professional.
The slides, worksheet, lesson plan and poster for this lesson are free to download and free to use in your course — no sign-up, no permission needed. See the teacher resources →
Assign this lesson to your class:
Using Canvas, Blackboard or Moodle? Copy the link and paste it into your course page or assignment. More ways to add lessons to your LMS.

